| boot | Boot path (BIOS + UEFI via bootloader crate) | VERIFIED |
| serial | Serial console & structured boot stages | VERIFIED |
| cpu | CPU identification | VERIFIED |
| memory-physical | Physical memory manager | VERIFIED |
| memory-virtual | Virtual memory / paging (kernel + user W^X) | VERIFIED |
| heap | Kernel heap allocator | VERIFIED |
| interrupts | GDT/IDT, exceptions, PIT timer (via I/O APIC) | VERIFIED |
| scheduler | Preemptive process scheduler | VERIFIED |
| preemption | Timer-driven Ring 3 preemption | VERIFIED |
| vfs | VFS & embedded initramfs | VERIFIED |
| shell | Interactive serial shell | VERIFIED |
| elf-loader | ELF64 loader (strict validation, W^X) | VERIFIED |
| ring3 | Ring 3 execution & privilege isolation | VERIFIED |
| syscalls | Syscall ABI (write/exit/yield/getpid/spawn/wait/msg/gui) | VERIFIED |
| process | Process lifecycle & crash containment | VERIFIED |
| process-isolation | Per-process page tables & concurrency | VERIFIED |
| ipc | IPC message channels | VERIFIED |
| pci | PCI enumeration | VERIFIED |
| block | Block-device abstraction (read + write) | VERIFIED |
| nvme | NVMe driver (read + write + flush) | VERIFIED |
| filesystem | ITFS persistent filesystem | VERIFIED |
| graphics | Framebuffer graphics (back buffer, font, primitives) | VERIFIED |
| compositor | Window compositor (per-window buffers, ownership isolation) | VERIFIED |
| gui-syscalls | GUI syscalls (validated Ring 3 window rendering) | VERIFIED |
| input-keyboard | PS/2 keyboard input (IRQ1) | VERIFIED |
| input-mouse | PS/2 mouse input (IRQ12) | VERIFIED |
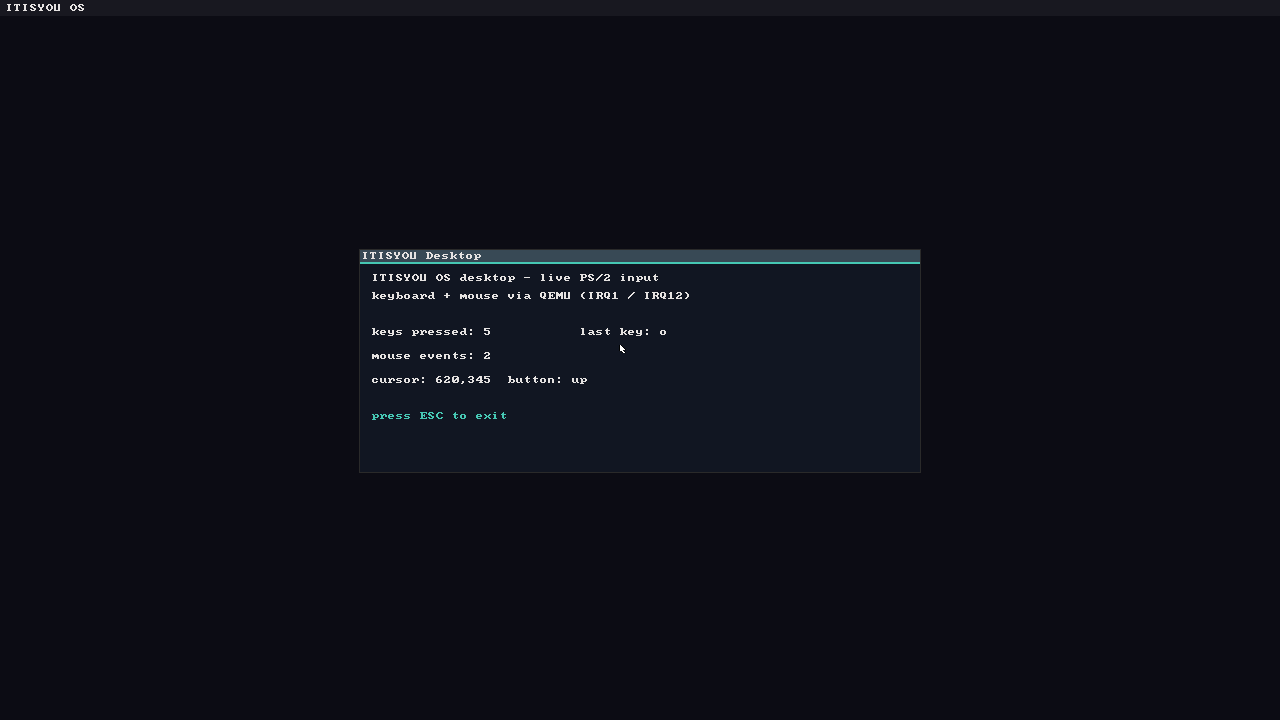
| desktop | Interactive desktop (live keyboard + mouse) | VERIFIED |
| device-model | Device/driver model (probe/bind, device table) | VERIFIED |
| pci-caps | PCI BAR sizing + capability walking (MSI/MSI-X/PCIe/PM) | VERIFIED |
| usb-uhci | USB UHCI host controller (control transfers, enumeration) | VERIFIED |
| usb-hid | USB HID keyboard input (interrupt endpoint) | VERIFIED |
| input-unified | Unified input events (PS/2 + USB HID) | VERIFIED |
| audio-ac97 | AC97 audio output (PCM DMA, samples verified) | VERIFIED |
| devinfo-syscall | Userspace device access syscall (least authority) | VERIFIED |
| capabilities | Capability model (default deny, no amplification) | VERIFIED |
| fs-sandbox | Filesystem sandbox (traversal-proof path prefixes) | VERIFIED |
| services | Service supervisor (ordering, restart policy, diagnostics) | VERIFIED |
| app-model | Application manifests + platform launch (least privilege) | VERIFIED |
| packages | ITPKG packages (SHA-256 integrity + Ed25519 authenticity) | VERIFIED |
| updates | Atomic updates + rollback + reboot-proven recovery | VERIFIED |
| audit | Audit/provenance trail, hash-chained and persistent | VERIFIED |
| net-stack | IPv4 networking: e1000, ARP, ICMP, UDP, DNS | VERIFIED |
| net-sockets | Capability-scoped Ring 3 UDP sockets | VERIFIED |
| net-tcp | TCP streams from Ring 3 (retransmission, verified against the host TCP stack) | VERIFIED |
| net-dhcp | DHCP client (lease applied, verified against QEMU) | VERIFIED |
| fs-write | Capability-scoped userspace filesystem writes (atomic) | VERIFIED |
| hardening | SMEP/SMAP/UMIP, W^X, stack guard, pointer validation | VERIFIED |
| usb-xhci | USB xHCI host controller (enumeration + HID) | VERIFIED |
| irq-apic | Local APIC + I/O APIC line routing (8259 PIC retired) + MSI-X | VERIFIED |
| storage-second-driver | Second block-device backend (AHCI/virtio) | PLANNED |
| test-harness | QEMU boot/regression harness (serial + monitor + audio/USB) | VERIFIED |
| pkg-signing | Ed25519 package signatures + trusted-key verification | VERIFIED |
| acpi | ACPI discovery (RSDP/XSDT/MADT/FADT, validated) | VERIFIED |
| power-s5 | ACPI S5 soft power-off | VERIFIED |
| net-ipv6 | IPv6 foundations (NDP, SLAAC, ICMPv6) | VERIFIED |
| pkg-keys | Signing-key hierarchy (offline root, scoped certificates, signed revocation) | VERIFIED |
| release-artifact | Reproducible, checksummed public boot images | VERIFIED |
| proc-args | Program arguments for Ring 3 programs (V0.10) | VERIFIED |
| fs-reclaim | ITFS space reclamation, no format change (V0.10) | VERIFIED |
| task-stack-guards | Guard pages for kernel task stacks (V0.10) | VERIFIED |
| always-on-sched | Always-on co-scheduling at audited safe points (V0.10) | VERIFIED |
| process-tree | Process tree: parent-only wait, wait_nohang, sleep, orphans, ps/kill (V0.10) | VERIFIED |
| userspace-init | /sbin/init as pid 1 from /etc/init.conf, restarted by the kernel (V0.10) | VERIFIED |
| svc-report | Kernel service table fed by kernel-checked supervisor reports (V0.10) | VERIFIED |
| ring3-shell | Ring 3 shell with the console’s input (V0.10) | VERIFIED |
| desktop-apps | Ring 3 desktop apps with click-to-focus and routed input (V0.10) | VERIFIED |
| user-copy-hardening | Kernel copies refuse user memory the program cannot write (V0.10) | VERIFIED |
| audit-integrity | Audit trail and package store kernel-owned, echoes escaped, a stored trail that verifies across boots (V0.11) | VERIFIED |
| sys-view | Approved read-only system view, console-granted only (V0.11) | VERIFIED |
| diag-model | Pinned diagnostic model, trained at build time from synthetic scenarios (V0.11) | VERIFIED |
| inference-service | Ring 3 inference service (inferd) outside the kernel (V0.11) | VERIFIED |
| diag-agent | Diagnostic agent with runbooks and no authority to act (V0.11) | VERIFIED |
| proposals | Kernel-checked proposals; approve and deny only at the console (V0.11) | VERIFIED |
| verified-actions | Approved actions executed, verified and rolled back by the kernel (V0.11) | VERIFIED |
| output-escaping | Ring 3 output cannot drive the operator’s terminal (V0.11) | VERIFIED |
| ipc-scoping | IPC authority scoped to named channels (V1.0) | VERIFIED |
| sysfuzz | Ring 3 syscall fuzzer — no sequence crashes or hangs the kernel (V1.0) | VERIFIED |
| decoder-fuzz | Every untrusted-byte decoder mutation-fuzzed (V1.0) | VERIFIED |
| cpu-containment | Every CPU exception from Ring 3 contained; user FPU off (V1.0) | VERIFIED |
| soak-leak | Long use leaks nothing in the kernels own accounting (V1.0) | VERIFIED |
| attack-surface-review | Whole-attack-surface adversarial review, findings verified and fixed (V1.0) | VERIFIED |